ISO 31000 Risk management process
The international risk management standard, ISO 31000:2018 Risk management — Guidelines, provides guidelines on managing risk. These guidelines can be customised to any situation and applied to any activity, including decision-making.
ISO 31000 can be used by anyone – individuals, groups of people, families, teams, organisations and governments – who wants to:
- Create and protect value by managing risks.
- Making decisions.
- Setting and achieving objectives.
- Improving performance.
In the context of this risk management standard, ‘risk’ is defined as ‘the effect of uncertainty on objectives’. The notion of risk is closely linked to uncertainty.
Risk can only be meaningfully defined in relation to objectives because it relates to the effect of uncertainty on objectives that have a potential consequence – good or bad – on your success.
It cannot exist in a vacuum. It must exist in relation to the achievement of your objectives.
The simplest definition of risk is “uncertainty that matters”. Risk can affect one or more of your objectives, or what might happen.
To the extent practicable, your objectives should be:
- specific;
- measurable either qualitatively or quantitatively;
- achievable within the constraints imposed by the context;
- relevant to the larger goals or context; and
- achievable within a stated time frame.
Organisations of all types and sizes face external and internal factors and influences that make it uncertain whether they will achieve their objectives.
Managing risk is iterative. It assists organisations in setting strategy, achieving objectives and making informed decisions. It is part of governance and leadership and is fundamental to how an organisation is managed at all levels.
The management of risk enables you to, for example:
- increase the likelihood of achieving objectives;
- encourage proactive management;
- be aware of the need to identify and treat risk throughout the organisation;
- improve the identification of opportunities and threats;
- comply with relevant legal and regulatory requirements and international norms;
- improve mandatory and voluntary reporting;
- improve governance;
- improve stakeholder confidence and trust;
- establish a reliable basis for decision making and planning;
- improve controls;
- effectively allocate and use resources for risk treatment;
- improve operational effectiveness and efficiency;
- enhance health and safety performance, as well as environmental protection;
- improve loss prevention and incident management;
- minimise losses;
- improve organisational learning; and
- improve organisational resilience.
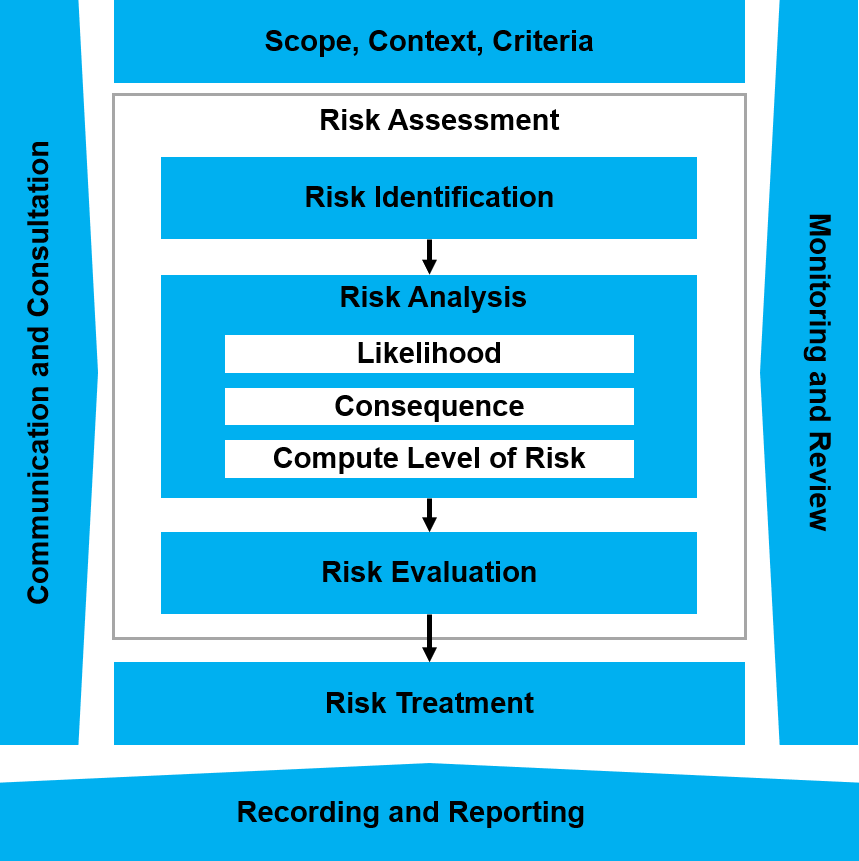
Managing risk is based on the risk management process. The risk management process involves the systematic application of policies, procedures and practices to the activities of communicating and consulting, establishing the context and assessing, treating, monitoring, reviewing, recording and reporting risk.
It comprises the activities described in the diagram shown below.
Properly designed and implemented, your risk management framework will ensure that the risk management process is a part of all activities throughout the organisation, including decision-making, and that changes in external and internal contexts will be adequately captured. A risk management framework set of components that provide the foundations and organisational arrangements for designing, implementing, monitoring, reviewing and continually improving risk management throughout the organisation.
Your risk management activities should be an integral part of management and decision-making and integrated into the structure, operations and processes of an organisation. It can be applied at strategic, operational, programme or project levels.
There can be many applications of the risk management process. But it must be customised to achieve objectives and to suit the external and internal context in which it is applied.
The dynamic and variable nature of human behaviour and culture should be considered throughout your risk management process.
Although the risk management process is often presented as sequential steps, in practice, they are iterative activities.
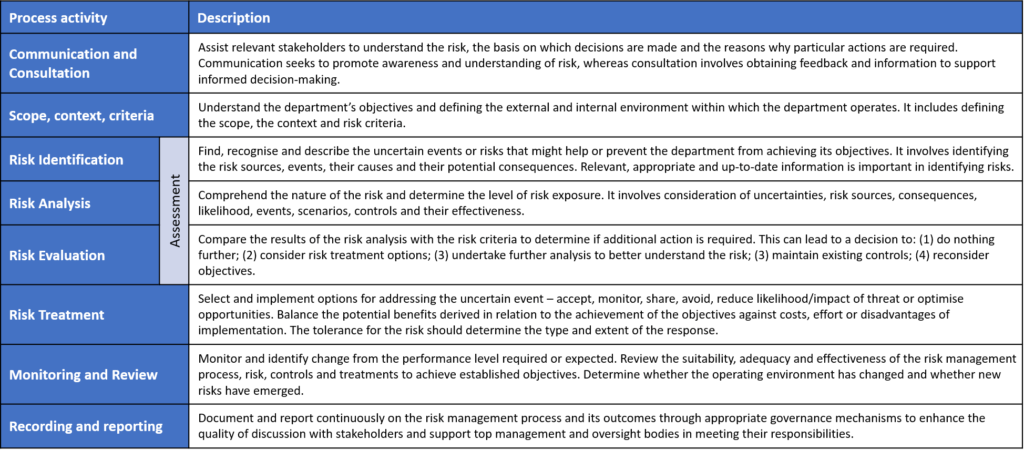
A summary of the key activities for the risk management process is shown in the table below.
Communication and consultation
Effective communication and consultation are essential to ensure that those responsible for identifying and managing risks and those with a vested interest understand the basis on which risk-informed decisions are made and reasons why particular actions and treatments are selected.
The purpose of communication and consultation is to assist relevant stakeholders in understanding risk, the basis on which decisions are made and the reasons why particular actions are required. It is a continual and iterative process to provide, share or obtain information, and to engage in dialogue with stakeholders regarding the management of risk.
A stakeholder is a person or organisation that can affect, be affected by, or perceive themselves to be affected by a decision or activity.
Communication seeks to promote awareness and understanding of risk, whereas consultation involves obtaining feedback and information to support decision-making.
Consultation is a two-way process of informed communication between an individual or organisation and its stakeholders on an issue before making a decision or determining a direction on that issue. It is:
- a process which impacts a decision through influence rather than power; and
- an input to decision making, not joint decision making.
Close coordination between two stakeholders should facilitate the factual, timely, relevant, accurate and understandable exchange of information, considering the confidentiality and integrity of information as well as the privacy rights of individuals. The information can relate to the existence, nature, form, likelihood, significance, evaluation, acceptability and treatment of the management of risk.
Communication and consultation with appropriate external and internal stakeholders should take place within and throughout all activities of the risk management process.
Risk management is enhanced through effective communication and consultation when all parties and stakeholders understand each other’s perspectives and, where appropriate, are actively involved in the decision-making process.
A collaborative and consultative approach is more likely to:
- Help establish the context appropriately and ensure that the interests of all stakeholders are understood and considered.
- Ensure that uncertainties, risks, issues and opportunities are adequately identified and managed.
- Bring together different areas of expertise when assessing or analysing risks to ensure different, and sometimes opposing, views are appropriately considered when defining the risk criteria and when assessing risks.
- Help secure endorsement, support and commitment for a treatment plan.
- Enhance any change management processes associated with making risk-informed decisions.
Methods of communication and consultation may include meetings, reports, on-line communication systems and learning packages, newsletters and flow charts.
Scope, context and criteria
The purpose of establishing the scope, the context and criteria is to customise the risk management process and enabling effective risk assessment and appropriate risk treatment.
Defining the scope
You should define the scope of your risk management activities.
As your risk management activities may be applied at different levels (e.g. strategic, operational, programme, project, or other activities), it is important to be clear about the scope under consideration, the relevant objectives to be considered and their alignment with your objectives.
When planning the approach, considerations include:
- Objectives and decisions that need to be made.
- Outcomes expected from the activities.
- Time, location, specific inclusions and exclusions.
- Appropriate risk assessment tools and techniques.
- Resources required, responsibilities and records to be kept.
- Relationships with other projects, processes and activities.
External and internal context
Your external and internal context is the environment in which you seek to define and achieve your objectives.
The context of your risk management activities should be established from the understanding of the external and internal environment in which you operate in. It should reflect the specific environment to which the risk management activities are to be applied.
Establishing the context sets the structure and foundation within which the risk assessment should be undertaken. It ensures that reasons for carrying out the risk assessment are clear. It also provides the backdrop of circumstances against which risks can be identified and assessed.
Understanding the context is important because:
- Risk management takes place in the context of your objectives and activities.
- Your individual, team or organisational factors can be a source of uncertainty, risk and opportunity.
- The purpose and scope of the risk management process may be interrelated with your objectives.
Defining risk criteria
You should specify the amount and type of risk that you may or may not take, relative to your objectives.
Risk criteria are the terms of reference against which the significance of a risk is determined. It is a set the criteria for:
- Deciding whether a risk or an opportunity can be accepted in pursuit of your objectives.
- Sometimes referred to as risk appetite, it specifies a technique to determine the magnitude of risk, or a parameter related to risk, together with a limit beyond which risk becomes unacceptable.
- The acceptability of risk can also be defined by specifying the acceptable variation in specific performance measures linked to objectives.
- Different criteria might be specified according to the type of consequence. For example, the criteria for accepting financial risk may differ from those defined for risk to human life.
- Evaluating the significance of a risk.
- An evaluation of the significance of a risk compared to other risks is often based on an estimate of the magnitude of risk compared with criteria which are directly related to thresholds set around your objectives.
- Comparison with these criteria can inform you which risks should be focused on for treatment, based on their potential to drive outcomes outside of thresholds set around objectives.
- The magnitude of risk is seldom the only criterion relevant to decisions about the significance of a risk. Other relevant factors can include sustainability (e.g. triple bottom line) and resilience, ethical and legal criteria, the effectiveness of controls, the maximum impact if controls are not present or fail, the timing of the consequences, the costs of controls and stakeholder views.
- Deciding between options.
- An organisation will be faced with many decisions where several, often competing, objectives are potentially affected, and there are both potential adverse outcomes and potential benefits to consider. For such decisions, several criteria might need to be met and trade-offs between competing objectives might be required.
- Criteria relevant to the decision should be identified. How the criteria are to be weighted or trade-offs made should be decided and accounted for.
- In setting criteria, the possibility that costs and benefits may differ for different stakeholders should be considered.
- The way in which different forms of uncertainty are to be taken into account should be decided.
This is where your attitude, appetite and tolerance for risk come in.
- Risk attitude is your approach to assess and eventually pursue, retain, take or turn away from risk.
- Risk appetite is the amount and type of risk that you are willing to pursue or retain to achieve our objectives and outcomes.
- Risk tolerance is your readiness to bear the risk after risk treatments are implemented to achieve your objectives and outcomes.
While criteria should be established at the beginning of the risk assessment process, they are dynamic and should be continually reviewed and amended, if necessary.
To set the criteria to evaluate the significance of a risk and to support decision-making processes, the following should be considered:
- The nature and type of uncertainties, risks and opportunities that can affect outcomes and objectives (both tangible and intangible).
- How consequences – both positive and negative – and likelihood will be defined and measured.
- Time-related factors.
- Consistency in the use of measurements.
- How the level of risk is to be determined.
- How combinations and sequences of multiple risks will be taken into account.
- The capacity to manage risks.
Risk assessment
Risk assessment is the overall process of:
- Risk identification – A process of finding, recognising and describing risks.
- Risk analysis – A process to comprehend the nature of risk and to determine the level of risk.
- Risk evaluation – A process of comparing the results of risk analysis with risk criteria to determine whether the risk and/or its magnitude is acceptable or tolerable.
Risk assessment should be conducted systematically, iteratively and collaboratively. This activity draws on the knowledge and views of stakeholders. It should use the best available information, supplemented by further enquiry as necessary.
Successful risk assessment is dependent on effective communication and consultation with internal and external stakeholders.
Involving stakeholders during the risk assessment activity will assist in:
- Ensuring that the interests of stakeholders are well understood and considered.
- Bringing together different areas of expertise for identifying and analysing risk.
- Ensuring that different views and concerns are appropriately considered when evaluating risks.
- Ensuring that risks, issues and opportunities are adequately identified.
The risk assessment activity provides decision-makers and stakeholders with an understanding of uncertainties, risks and opportunities that could affect the achievement of your objectives and adequacy and effectiveness of controls already in place.
Outputs from the risk assessment activity are inputs to decision-making processes and provide the basis for decisions about the most appropriate approach to be used to treat the risks or take advantage of the opportunity.
IEC 31010:2019 Risk management — Risk assessment techniques, an international risk assessment standard, provides further guidance on the selection and application of various techniques that can be used to help you improve the way uncertainty is taken into account and to help you understand uncertainties, risks and opportunities.
The techniques described in the standard provide a means to improve understanding of uncertainty and its implications for your decisions and actions. It can assists you in making decisions where there is uncertainty, to provide information about particular risks and as part of a process for managing risk.
IEC 31010:2019 categorises techniques according to their primary application in assessing risk, namely:
- eliciting views from stakeholders and experts, (Clause B.1);
- identifying risk;
- determining sources and causes (or drivers of risk);
- analysing existing controls;
- understanding consequences and likelihood;
- analysing dependencies and interactions;
- providing measures of risk;
- evaluating the significance of a risk;
- selecting between options; and
- recording and reporting.
Risk identification
The purpose of risk identification is to find, recognise and describe risks that might help or prevent you from achieving your objectives.
Identifying risk enables uncertainty to be explicitly taken into account. All sources of uncertainty and both beneficial and detrimental effects might be relevant, depending on the context and scope of the assessment.
Risk identification involves the identification of risk sources, events, their causes (drivers of risk) and their potential consequences. A risk source is an element which alone or in combination has the intrinsic potential to give rise to risk. An event (or incident or accident) is an occurrence or change of a particular set of circumstances. It can be one or more occurrences and can have several causes.
Identify what might happen (known uncertainties) or what situations exist that might affect the achievement of objectives and outcomes.
This includes identifying risks that are associated with not pursuing an opportunity. This is the risk of doing nothing and potentially missing out on an opportunity to improve performance.
In identifying the risk, consider the following:
- What could happen – What might go wrong? What might prevent the achievement of objectives? What risks could threaten your intended outcomes?
- How could it happen – Is the risk likely to occur at all or happen again? If so, what could cause the risk event from occurring?
- Where could it happen – Is the risk likely to occur anywhere, in any environment or place? Or is it a risk that is dependent on your location, physical area or activity?
- Why might it happen – What factors would need to be present for the risk event to occur again? Understand why a risk event might occur or be repeated.
- What might be the consequence – If the risk event were to eventuate, what consequences would, or might this have on objective and outcome? Will the consequence be felt locally, or will it impact on the whole organisation?
- Who does or can influence the outcome – How much is within your control or influence? Make sure that those with delegations, control, influence, resources and budgets are informed. This becomes more important when considering the treatments for the risk.
- Who is the risk owner – A risk owner is a person or entity with the accountability and authority to manage the risk and coordinate activities with control and treatment owners.
Relevant, appropriate and up-to-date information is important in identifying risks.
The following factors, and the relationship between these factors, should be considered during the risk identification activity:
- tangible and intangible sources of risk;
- causes (risk drivers) and events;
- threats and opportunities;
- vulnerabilities and capabilities;
- changes in the external and internal context;
- indicators of emerging uncertainties and risks;
- the nature and value of assets and resources;
- consequences and their impact on objectives;
- limitations of knowledge and reliability of information;
- time-related factors; and
- biases, assumptions and beliefs of those involved.
Consideration should be given that there may be more than one type of outcome, which may result in a variety of tangible or intangible consequences.
Once a risk is identified, identify any existing controls such as design features, people, processes and systems.
Risk analysis
The purpose of risk analysis is to comprehend the nature of the identified risk and its characteristics including, where appropriate, the level of risk.
Level of risk, or risk rating, is the magnitude of a risk or combination of risks, expressed in terms of the combination of consequences and their likelihood.
The risk analysis activity involves a detailed consideration of uncertainties, sources, causes (drivers of risk), consequences, likelihood, events, scenarios, controls and their effectiveness. An event can have multiple causes and consequences and can affect multiple objectives.
Risk analysis can be undertaken with varying degrees of detail and complexity, depending on the purpose of the analysis, the availability and reliability of the information, and the resources available.
Your analysis techniques can be qualitative, quantitative or a combination of these, depending on the circumstances and intended use.
Risk analysis should consider factors such as:
- the likelihood of events and consequences;
- the nature and magnitude of consequences;
- complexity and connectivity;
- time-related factors and volatility;
- the effectiveness of existing controls; and
- sensitivity and confidence levels.
Risk can be associated with several different types of consequences, impacting different objectives. Consequences might also change over time. For example, the adverse impacts of a fault might become more severe the longer the fault exists. Sometimes consequences result from exposures to multiple sources of risk.
Likelihood can refer to the likelihood of an event or the likelihood of a specified consequence. The parameter to which a likelihood value applies should be explicitly stated. The event or consequence whose likelihood is being stated should be clearly and precisely defined.
There are usually many interactions and dependencies between uncertainties, risks and opportunities. For example, multiple consequences can arise from a single cause or a particular consequence might have multiple causes.
Existing controls and their effectiveness must be taken into account during this risk analysis activity as the level of risk will depend on their adequacy and effectiveness.
Control is something that is currently in place that is reducing the risk. It is often brought in as a result of a previous situation or incident.
There are three categories of controls:
- Preventative – To reduce the likelihood of a situation occurring including policies and procedures, approvals, authorisations, police checks and training. These controls generally target the causes or drivers of a risk event.
- Detective – To identify failures in the current control environment including performance reviews, reconciliations, audits and investigations.
- Corrective – To reduce the consequence and rectify a failure after it has been discovered including the crisis management and business continuity plans, insurance and disaster recovery plans. These controls generally target the potential consequences of a risk event.
Risk is affected by the overall effectiveness of any controls that are in place. The following aspects of controls should be considered:
- the mechanism by which the controls are intended to modify risk;
- whether the controls are in place, are capable of operating as intended, and are achieving the expected results;
- whether there are shortcomings in the design of controls or the way they are applied;
- whether there are gaps in controls;
- whether controls function independently, or if they need to function collectively to be effective;
- whether there are factors, conditions, vulnerabilities or circumstances that can reduce or eliminate control effectiveness including common cause failures; and
- whether controls themselves introduce additional risks.
Any assumptions made during risk analysis about the actual effect and reliability of controls should be validated where possible, with an emphasis on individual or combinations of controls that are assumed to have a substantial modifying effect. This should consider information gained through routine monitoring and review of controls.
In many cases these situations or incidents arise, not because of a lack of controls, but because of failure of existing controls.
The real key to managing risks effectively is to ensure that your existing controls are effective by considering the following:
- What are the existing controls for a particular risk event?
- Are those controls capable of adequately managing or treating the risk event so that it is controlled to a level that is tolerable or acceptable?
Your risk analysis activity may be influenced by any divergence of opinions, biases, perceptions of risk and judgements.
Additional influences are the quality of the information used, the assumptions and exclusions made, any limitations of the techniques and how they are executed. These influences should be considered, documented and communicated to decision-makers.
The risk analysis activity provides an input to risk evaluation, to decisions on whether risk needs to be treated and how, and on the most appropriate risk treatment strategy and methods. The results provide insight for decisions, where choices are being made, and the options involve different types and levels of risk.
Risk evaluation
The purpose of risk evaluation is to support decisions.
Risk evaluation involves comparing the results of the risk analysis with the established risk criteria to determine where additional action is required. This activity uses the understanding of risk obtained during risk analysis to make risk-informed decisions about potential future actions. Ethical, legal, financial and other considerations, including perceptions of risk, are also inputs into the decision-making process.
This can lead to a decision to:
- do nothing further;
- consider risk treatment options;
- undertake further analysis to better understand the risk;
- maintain existing controls; or
- reconsider objectives.
The information from risk identification and analysis can be used to conclude whether the risk should be accepted and the comparative significance of the risk relative to the objectives and performance thresholds.
This provides input into decisions about whether a risk is acceptable or requires treatment and any priorities for treatment. Decisions should take account of the wider context and the actual and perceived consequences to external and internal stakeholders.
A risk may be acceptable or tolerable in the following circumstances:
- no treatment is available;
- treatment costs are prohibitive or uneconomical;
- the level of risk is low and does not warrant using resources to treat the risk;
- opportunities involved significantly outweigh the threats; or
- a conscious decision has been made not to treat it.
Factors other than the magnitude of risk that can be taken into account in deciding priorities include:
- other measures associated with the risk such as the maximum or expected consequences or the effectiveness of controls;
- the qualitative characteristics of events or their possible consequences;
- the views and perceptions of stakeholders;
- the cost and practicability of further treatment compared with the improvement gained; or
- interactions between risks including the effects of treatments on other risks.
The outcome of risk evaluation should be recorded, communicated and then validated at appropriate levels of the organisation.
Once risks have been evaluated and treatments decided, the risk assessment activity can be repeated to check that proposed treatments have not created additional adverse risks and that the risk remaining after treatment is within your risk appetite.
Risk treatment
The purpose of risk treatment is to select and implement options for addressing risk. Having completed a risk assessment, treating a risk involves selecting and implementing one or more treatment options that will change the likelihood of occurrence, the consequences of the risk, or both.
Risk treatment involves an iterative process of:
- formulating and selecting risk treatment options;
- planning and implementing risk treatment;
- assessing the effectiveness of that treatment;
- deciding whether the remaining risk is acceptable; and
- if not acceptable, taking further treatment.
Selecting the most appropriate risk treatment option involves balancing the potential benefits derived in